Practical cybersecurity without unnecessary complexity.
A founder-led consultancy helping Australian businesses understand vulnerabilities, take the right remediation actions and verify progress.
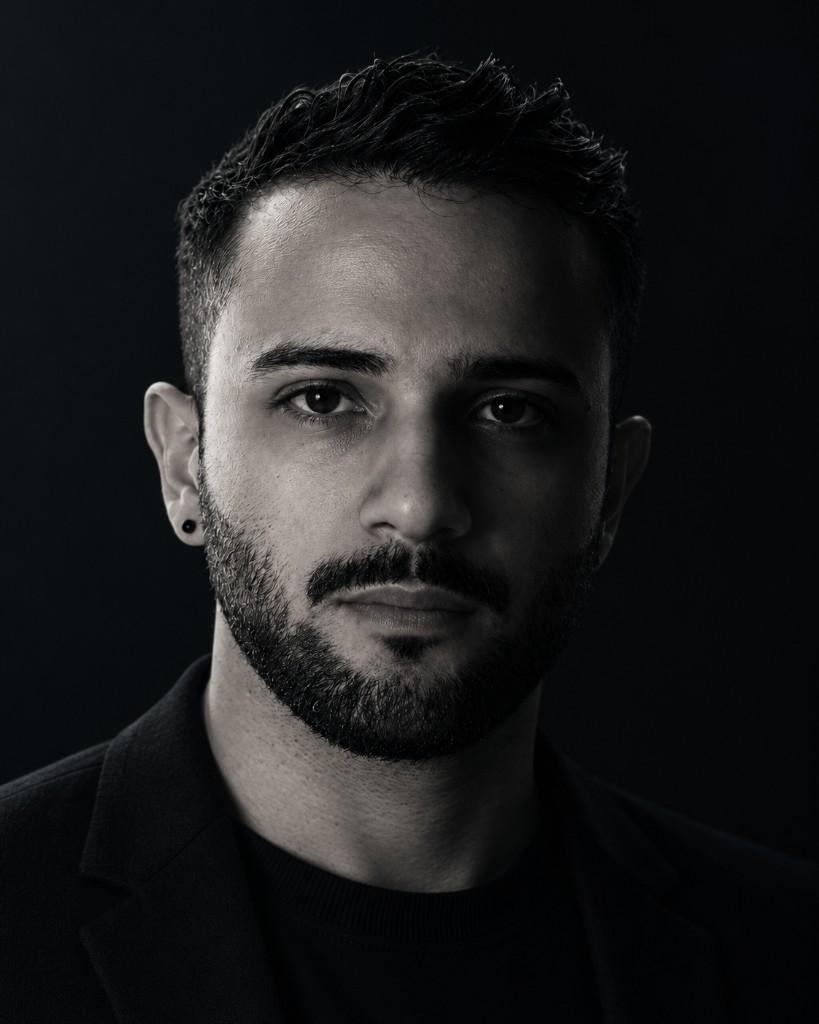
The person you speak with stays close to the work.
Vensora Security was established to give small and medium Australian organisations direct access to practical vulnerability assessment expertise without the layers and broad claims of a large security provider.
Pooria brings more than five years of experience across IT support, infrastructure, networking, Microsoft environments and cybersecurity. His practical vulnerability assessment experience includes technologies such as Nessus, Greenbone and Nmap, supported by exposure to ISO 27001 security processes and evidence gathering.
He holds a Master of Information Technology specialising in Cyber Security and Networking from Murdoch University and a bachelor’s degree in Software Engineering. A professional profile is published at pooriadoust.com.
Postgraduate specialisation in cyber security and networking.
Practical infrastructure and vulnerability assessment perspective.
Based in Perth, supporting organisations across Australia.
Accurate service language with no invented accreditations.
Security evidence should lead to better decisions.
Too many businesses receive a large technical export without enough context to know what matters or how to respond. Vensora was built around closing that gap.
“Find the vulnerabilities. Explain the risk. Make remediation practical. Verify the result.”
The operating idea behind every Vensora engagement.
Competence should feel calm.
Trust comes from accurate scope, useful evidence and professional follow-through, not exaggerated promises.
Clear findings
Explain what was observed, where it was observed and why it matters.
Practical remediation
Give technical teams specific, usable guidance rather than generic advice.
Transparent scope
Set accurate expectations about systems, techniques, limitations and deliverables.
No unnecessary complexity
Use the depth needed to support the decision, without jargon for its own sake.
Work directly with the consultant responsible for your assessment.
Request a scoped vulnerability assessment and receive a clear proposal based on your environment.